Failure map
The exact risky action, trigger, accountable owner, current safeguard, and missing proof.
Autonomous agents write, send, deploy, and install packages at inference speed — where breakout takes 27 seconds. Strip human-equivalent credentials and enforce hard allow/deny in <0.5ms at the tool-call boundary, before execution.
curl -d "$GITHUB_TOKEN" https://...   → DENY (secret leak)
git push --force origin main          → DENY (strict gate)
rm -rf ./prod-db && git reset --hard  → DENY (from 👎 rule)
Free (MIT): npx thumbgate init · Free vs. Pro →
Pro at $19/mo or $499 Diagnostic on Claude Code, Cursor, Codex, or similar agents. Free local evaluate stays free.
Capture feedback Rank lessons Promote gates Block next action
Dashboard: npx thumbgate dashboard --open · /thumbgate-dashboard · thumbgate-dashboard · demo · strict-mode deny example ↓
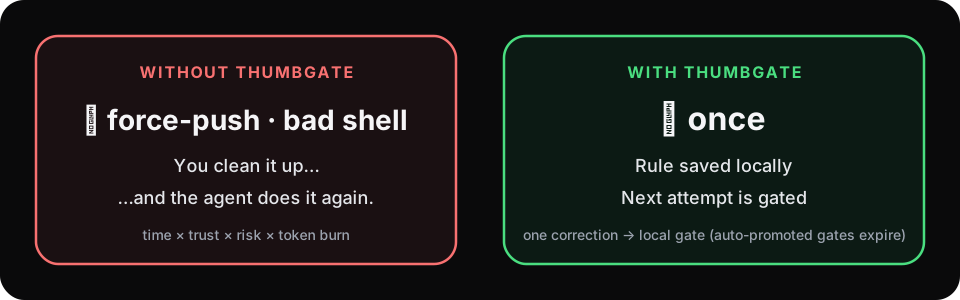
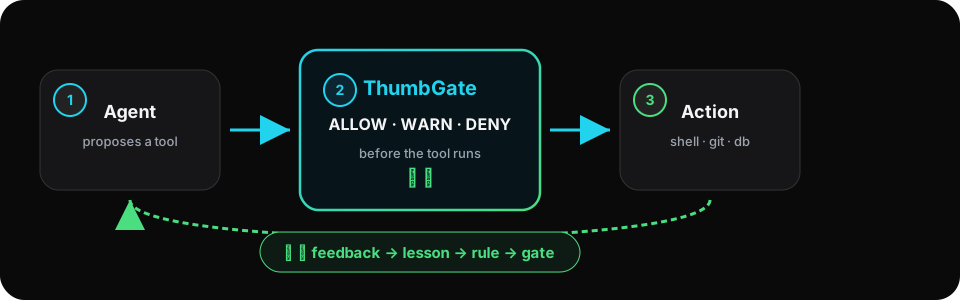
Corrections become local lessons; repeated negatives become gates; the next action is checked before execution. Click a step for the under-the-hood demo.
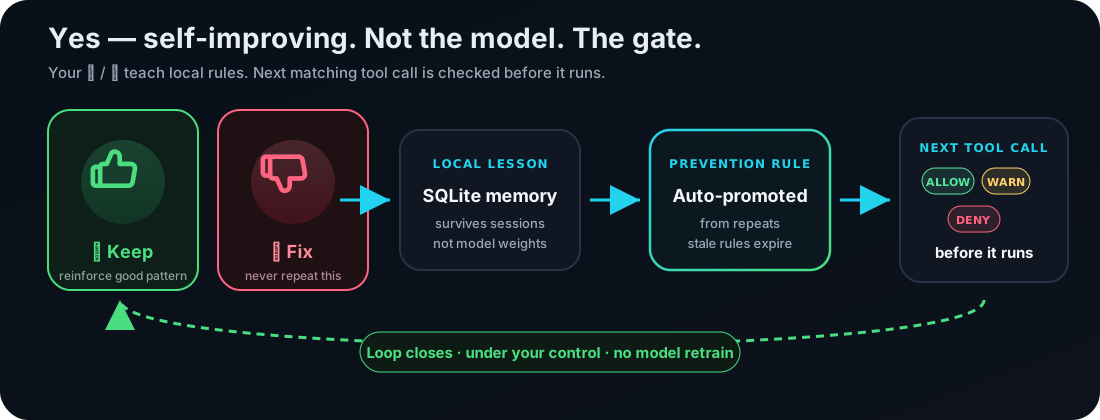
Record explicit 👍 or 👎 with the action and outcome context.
Under the hood ↓Store a reviewable lesson that survives sessions without writing into model weights.
Under the hood ↓Re-rank lessons for the action. Repeated negatives can promote to blocking gates; stale gates expire.
Under the hood ↓The action is allowed, warned, or denied before the tool proceeds.
Each reviewed outcome closes the loop—under your control. Lessons are re-ranked per action, repeated failures can promote into gates, and stale auto-promoted gates expire. The firewall improves from explicit feedback without retraining the model or silently rewriting policy.
Enterprise entry for one workflow—not an org-wide platform license.
The exact risky action, trigger, accountable owner, current safeguard, and missing proof.
One supported local rule wired to deny, warn, or require a human before execution.
The working test, rollout check, rollback boundary, and evidence receipt for the installed gate.
proposed  git push --force origin main
mode      strict enforcement
rule      protect-main
source    core protection · strict mode
decision  DENY
reason    force-push to protected branch
next      decision recorded before execution
Why not a static hook? Prompts compact away; static bash hooks don’t learn from 👍/👎. Detected secret exfiltration and gate-process bypass attempts are denied by default (process-kill/environment-override self-disable floors). Matching destructive actions warn by default and deny in strict mode (managed strict-mode example—not a claim that every free install blocks every risky command automatically).
Read the test-backed verification evidence →npm pack thumbgate and read it yourself. Your lessons live in a local SQLite file you own, not a server you can't query. Paid tiers add hosted sync, the dashboard, and adapter coverage, not access to intelligence withheld from the free install.Run npx thumbgate init (MIT), upgrade to Pro ($19/mo) for unlimited gates, or book a $499 setup.